Business.com aims to help business owners make informed decisions to support and grow their companies. We research and recommend products and services suitable for various business types, investing thousands of hours each year in this process.
As a business, we need to generate revenue to sustain our content. We have financial relationships with some companies we cover, earning commissions when readers purchase from our partners or share information about their needs. These relationships do not dictate our advice and recommendations. Our editorial team independently evaluates and recommends products and services based on their research and expertise. Learn more about our process and partners here.
Protect your online store and your customers' information with these 10 e-commerce security best practices, from choosing a secure platform to preventing cyberattacks.

Running an online store means handling customer information, processing payments and keeping your website up and running. It also means protecting your business against cybercriminals who may try to steal sensitive data, gain access to customer accounts or exploit weaknesses in your website. And this is a real concern: According to IBM’s 2026 X-Force Threat Intelligence Index, attackers exploited security vulnerabilities in 40 percent of the incidents IBM investigated in 2025.
Whether you’re launching your first e-commerce website or managing an established online store, security should be a priority. The following 10 best practices can help you protect your business, safeguard customer information and give shoppers greater confidence when buying from you.
E-commerce security helps prevent cyberattacks, protect sensitive customer information and reduce the risk of online payment fraud and unauthorized access. It also helps keep your online store running smoothly so customers can shop with confidence. Here are 10 security best practices to help safeguard your e-commerce business.
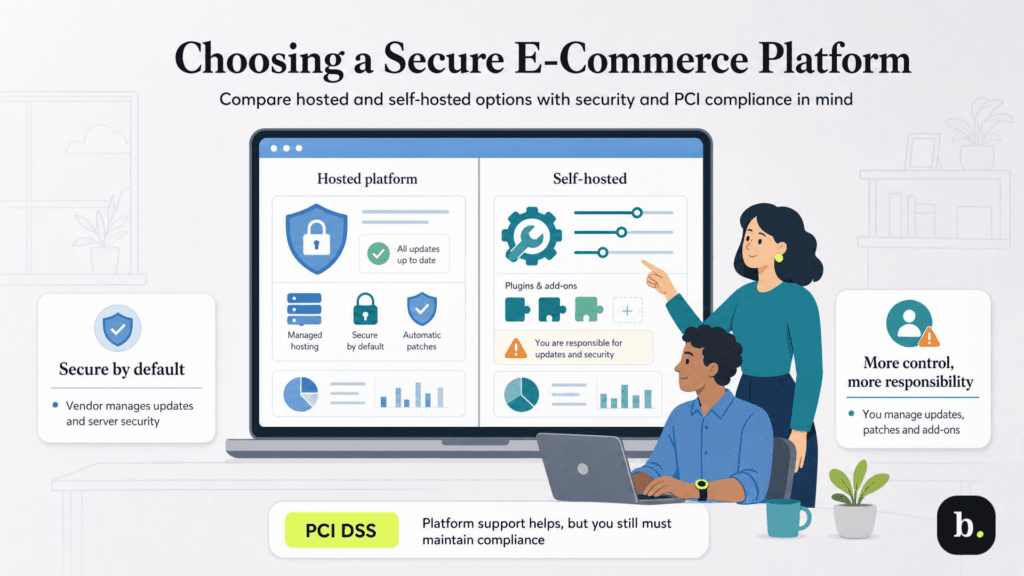
The first step in protecting your online store is choosing a reliable e-commerce platform. With hosted platforms, such as Shopify and Squarespace, the provider typically handles much of the technical security work, including server maintenance and updates. With self-hosted e-commerce software, such as WooCommerce, you’re generally responsible for more of these tasks yourself.
Look for a platform with strong security features, regular software updates and support for Payment Card Industry Data Security Standard (PCI DSS) compliance. This standard is designed to protect customers’ credit and debit card information when businesses accept, process or store card payments.
Keep in mind that using a PCI-compliant platform doesn’t automatically mean your business is PCI compliant. Depending on how you process payments, you may need to complete an annual self-assessment questionnaire or undergo additional security testing, such as quarterly vulnerability scans. Keeping your software, plugins and extensions up to date is also important, both for PCI compliance and general website security. Be sure to install security patches promptly to address newly discovered vulnerabilities.
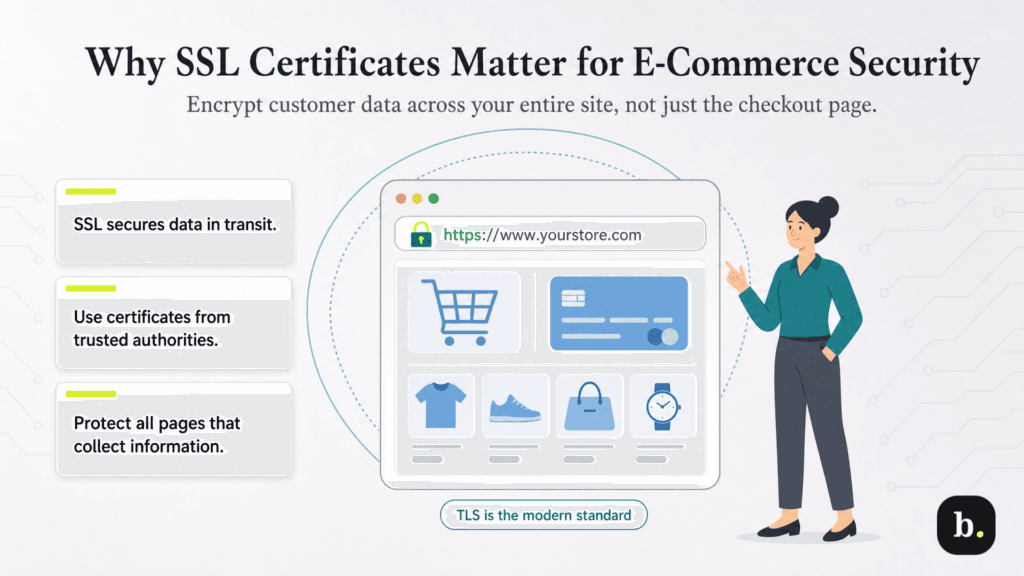
An SSL certificate helps verify your website’s identity and enables an encrypted connection between your e-commerce site and its visitors. This protects sensitive information, such as customer passwords and credit card details, as it travels between a shopper’s browser and your website. Although websites now use Transport Layer Security (TLS), the term SSL is still widely used. For information stored on your servers or in the cloud, additional protections such as cloud encryption can help keep sensitive data secure.
The good news is that you probably won’t have to pay extra for an SSL certificate if you use Shopify, Squarespace or another hosted e-commerce platform. It’s usually part of the package. If you’re running your own website, though, you’ll want to check with your hosting provider about getting a certificate. And don’t overlook the rest of your site. Your checkout page isn’t the only place where customers need a secure connection.
“Every e-commerce site should be using SSL, and that means using SSL certificates issued by a trusted certificate authority,” said Phil Brass, research consulting director at Atredis Partners, a provider of security assessments and advisory services. “Nobody should be sending payment data in plain text across the internet.”
Most browsers warn visitors when a website doesn’t have a secure connection, often with a message that says “Not secure.” That’s hardly what you want customers to see when they’re about to enter their credit card information. Of course, a secure connection doesn’t guarantee that a website is trustworthy, but it does help protect shoppers’ information and give them some peace of mind.
Stolen passwords can give cybercriminals access to your online store, customer accounts and sensitive business information. Even a strong password can be compromised through phishing attacks or data breaches. That’s why it’s important to add another layer of protection with multifactor authentication (MFA).
MFA requires users to verify their identity in at least two different ways before they can log in. For example, they might enter their password and then provide a code sent to their phone or generated by an authenticator app. Depending on the system, users may also be able to verify their identity through biometric authentication, such as a fingerprint or facial recognition. Even if someone manages to steal a password, that additional security measure can help keep them out of the account.
At a minimum, enable MFA for your store’s administrator and employee accounts, along with related accounts such as your business email, payment processor and domain registrar.
“Using multifactor authentication for your employees can be a great way to make it harder for threat actors to impersonate them,” Brass said. “Using special applications like Google Authenticator on a mobile device is also a good, strong measure.”
Using an authenticator app is generally safer than getting verification codes by text. Criminals can sometimes intercept text messages by taking control of someone’s phone number through a scam known as SIM swapping. With an app like Google Authenticator, the codes are generated right on your device and typically change every 30 seconds. That makes them harder to steal, although phishing scams can still trick people into giving them away.
If you or your employees work remotely, a virtual private network (VPN) can help protect sensitive business information, especially when you’re using public Wi-Fi. But VPNs can also be useful for controlling who gets into your company’s internal systems. A standard VPN service helps secure your connection when you’re working from a coffee shop, hotel or other public location. If you want to restrict access to your business network, though, you’ll generally need a VPN designed for that purpose.
“A VPN is an excellent tool for restricting access to networks and network services to only those people who are authorized,” Brass said. “If possible, even your website authoring platform should be protected by a VPN.”
If you have a self-hosted website, you can use a VPN to help control access to its administrative tools. Shopify and Squarespace users don’t have that same level of control, so it’s especially important to protect administrator accounts with multifactor authentication and use the security features available through those platforms. And regardless of how you run your store, don’t neglect the basics, including strong passwords. A VPN won’t protect you from every threat.
Businesses can choose from managed VPN services that charge a monthly fee per user. If you have IT support, free, open-source software such as OpenVPN is another option, although you’ll need the technical expertise to configure and maintain it.
Your employees handle sensitive customer information, and even a simple mistake can put that data at risk. Make sure everyone who works with customer accounts, payment information or your online store’s administrative tools understands your security policies. Train employees to recognize phishing emails, use strong passwords and avoid sharing sensitive information through unsecured email, text messages or chat.
Customers have a role to play in protecting their information, too. Encourage them to use strong, unique passwords for their accounts and be cautious about suspicious emails or messages claiming to come from your business. For example, let customers know that your business will never ask for their password or full payment details by email, text or phone. You should also explain how your company protects customer information and how shoppers can contact you if they notice suspicious activity. Being open about your security practices can help build trust with e-commerce customers and give them greater confidence when shopping on your site.
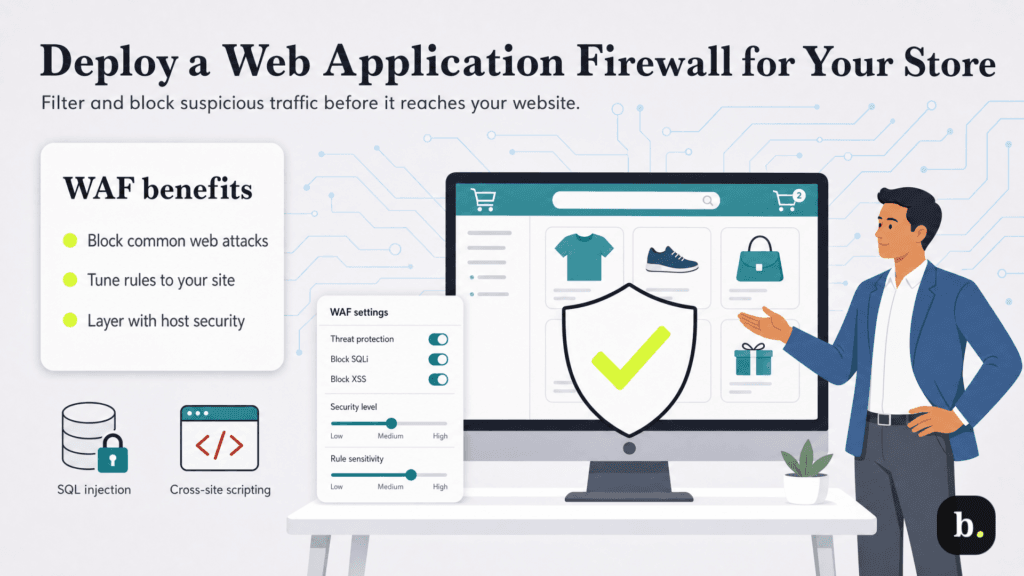
A web application firewall (WAF) watches the traffic coming into your website and helps stop suspicious requests before they cause trouble. For example, hackers may try to use SQL injection to get into your store’s database and steal customer information. Another common attack, called cross-site scripting, involves slipping malicious code into a website so it runs in visitors’ browsers. A WAF can help protect against both types of attacks, although it won’t catch everything.
Not all WAFs offer the same level of protection, however. “They vary in effectiveness, and will always be more effective if they are highly tuned to your site’s structure,” Brass said.
Many hosted e-commerce platforms already provide firewall protection as part of their security services. If you manage your own website, you may need to set up a WAF through your hosting provider or a third-party security service. Either way, it’s worth checking what protections are already in place and whether you need additional security measures. If you’re using a third-party WAF, a security professional can help you configure it properly.
If a cyberattack, technical failure or human error wipes out important information, having a recent backup can save your business a lot of trouble. Back up your website files, databases and other critical information regularly, and store copies in a secure location, such as a cloud storage service. Keep at least one copy somewhere attackers can’t easily reach, such as a separate account or offline storage, so ransomware can’t encrypt or delete it along with your site.
You have enough to keep track of when you’re running an online store, so automate your backups rather than adding another task to your to-do list. See if your hosting provider offers automatic backups or, if you’re using Shopify, look into apps that can back up your store’s data. Just don’t assume everything is working because you’ve set it up. Every so often, test whether you can actually restore your information. Finding out your backups are useless after you’ve lost important data is a headache you definitely don’t need.
When customers buy something from your online store, they trust you to keep their payment information safe. One way to reduce the risk of exposing sensitive credit card details is to use a secure payment gateway from a provider such as Stripe, PayPal or Square. These services can process transactions without requiring your business to handle or store customers’ card information directly. If you use a hosted platform like Shopify, payment processing may already be built in.
Brass said using a third-party payment provider can reduce your exposure to stolen card information. “Ideally, the e-commerce site never sees any payment card data at all. While this does reduce some of the direct risk to the business (nobody can steal the credit cards from your site or database), it really just moves that risk to the payment gateway.” That’s usually a worthwhile trade-off for small businesses. Established payment providers have security teams and resources that most online stores can’t match.
When choosing a payment provider, make sure it complies with the Payment Card Industry Data Security Standard (PCI DSS).
Think about the different people who work on your online store. Your customer service team needs to look up orders and help shoppers, but there’s no reason they should be able to make changes to your website’s code. With role-based access control (RBAC), you decide what each employee can access based on the work they do. That way, if someone gets hold of an employee’s login credentials, there’s a limit to how much damage they can do.
“If someone only needs to update product descriptions on their e-commerce site, they shouldn’t be able to modify payment systems,” said Simon Wijckmans, founder and CEO of cside. “When you combine this careful control over who can do what with active monitoring of your site’s activities, you create a much stronger security position.”
Most e-commerce platforms offer some way to manage staff permissions. Give employees access only to the tools and information they need to do their jobs, and give each person their own login rather than sharing a single admin account. Review permissions regularly, especially when employees change roles, and remove access immediately when someone leaves your business. It’s also worth monitoring administrative activity for unusual changes or unauthorized access.
Cybercriminals don’t always make their presence obvious. Some attacks can go unnoticed for months or even years, giving hackers plenty of time to steal sensitive information. “We’ve seen cases where malicious code ran undetected on e-commerce websites for over two years, quietly stealing customer data,” Wijckmans said. “Even more concerning, when attackers compromise one business, they often use it as a springboard to attack others.”
It’s worth paying attention to anything unusual happening on your website. Repeated failed login attempts, unfamiliar administrator accounts or changes to your checkout page that nobody authorized could all signal trouble. The same goes for customers reporting fraudulent charges after shopping at your store. Your e-commerce platform may have security monitoring features built in, or you can use separate tools to watch for suspicious activity. Set up alerts so you’re aware of potential problems before they get out of hand.
Of course, alerts won’t do much good if nobody follows up on them. As Brass pointed out, businesses need to pay attention to warnings from their firewalls, security software and other protective tools. Investigate suspicious activity promptly and have a plan for responding to potential breaches before they turn into bigger problems.
Customers expect their personal information to be safe when they shop online. If your website is compromised, the damage can go well beyond stolen data, affecting your finances, reputation and customer relationships. Here are four reasons why e-commerce security deserves your attention:
Cybercriminals are always looking for ways to exploit weaknesses in online stores, and even businesses that take security seriously can fall victim to an attack. It helps to be familiar with the tactics they use so you have a better chance of spotting trouble early. Here are some common e-commerce security threats.
Phishing scams use emails, text messages and phone calls to trick people into revealing sensitive information, such as passwords, account details or payment information. Cybercriminals may pose as your payment processor, e-commerce platform or another trusted company, often claiming there’s a problem with your account that needs immediate attention.
If you get an unexpected email or text asking you to click a link, open an attachment or share personal information, proceed with caution. Even if the message appears to come from a company you do business with, don’t use the links or phone numbers it provides. Go to the company’s official website or call a number you’ve used before to find out whether the message is legitimate.
Malware is malicious software that can steal sensitive information, disrupt your website or give hackers access to your systems. Ransomware is a type of malware that can lock you out of your files or encrypt your data until you pay a ransom. Both can cause serious problems for an online store, from lost sales to exposed customer information.
There are several ways malware and ransomware can find their way onto your systems. An employee might open an infected email attachment, click a malicious link or download software from an untrustworthy source. Hackers can also take advantage of security flaws in programs that haven’t been updated.
Keeping your software current and using reliable security tools can help, but it’s just as important to be careful about what you and your employees click and download. Regular backups can also help you recover from ransomware attacks without relying on criminals to restore your data. However, some attackers also steal sensitive information and threaten to release it unless you pay, something backups can’t prevent.
SQL injection attacks exploit weaknesses in how a website handles information entered into forms, search boxes and other fields. Hackers can use these vulnerabilities to send malicious commands to your website’s database, potentially gaining access to customer information, changing records or deleting important data.
This is primarily a concern for self-hosted websites and custom-built features, where businesses have more responsibility for keeping their code secure. To reduce your risk, keep your e-commerce software, plugins and extensions up to date. A web application firewall (WAF) can also help block suspicious requests, although it won’t catch every attack. If you have a web developer, ask about secure coding practices, such as parameterized queries, which help prevent attackers from manipulating database commands.
Cross-site scripting (XSS) attacks happen when hackers exploit a website vulnerability to inject malicious code that runs in visitors’ browsers. This can allow attackers to steal login information, hijack customer sessions or redirect shoppers to fraudulent websites. For an online store, that can mean compromised customer accounts and lost trust.
To reduce the risk, keep your e-commerce software and plugins updated, and make sure any custom website features are built with security in mind. Ask your web developer about using a Content Security Policy (CSP), which helps control what scripts can run on your website and limits the damage from certain XSS attacks.
E-skimming happens when cybercriminals secretly add malicious code to an online store’s checkout page to steal customers’ payment information. These attacks, sometimes called Magecart attacks, can go unnoticed because the checkout process may appear to work normally. Customers enter their credit card details, complete their purchases and have no idea their information has been stolen.
Some attackers go a step further. “Attackers create fake payment forms that overlay legitimate checkout pages,” Wijckmans said. “Customers think they’re entering their credit card details on a legitimate payment page, but they’re actually sending that information directly to criminals.”
To reduce the risk of e-skimming, keep your e-commerce software and plugins updated, restrict access to your website’s administrative tools and monitor your checkout pages for unauthorized changes. If you use third-party scripts for payment processing, analytics or other features, use reputable providers and check those scripts for unexpected changes. The latest PCI DSS requirements also address payment-page security, including monitoring scripts for unauthorized changes. Your responsibilities depend on how your checkout is set up.
Keeping your online store secure takes some ongoing attention, but you don’t have to tackle everything at once. Start with the basics, such as strong passwords, multifactor authentication and regular software updates. Then take a closer look at how your business handles customer information, processes payments and monitors suspicious activity. As your store grows, revisit your security measures to make sure they’re keeping up with your needs. A little prevention now can save you a lot of trouble down the road.
Amanda Clark and Sean Peek contributed to this article. Source interviews were conducted for a previous version of this article.