Business.com aims to help business owners make informed decisions to support and grow their companies. We research and recommend products and services suitable for various business types, investing thousands of hours each year in this process.
As a business, we need to generate revenue to sustain our content. We have financial relationships with some companies we cover, earning commissions when readers purchase from our partners or share information about their needs. These relationships do not dictate our advice and recommendations. Our editorial team independently evaluates and recommends products and services based on their research and expertise. Learn more about our process and partners here.
Set clear expectations for how employees use company technology, access business information and protect sensitive data.


Your employees rely on computers, smartphones, internet access and a growing number of apps to get their jobs done. But without clear guidelines, it’s easy for someone to download an unapproved program, store sensitive customer information in the wrong place or unknowingly put your business at risk. An acceptable use policy (AUP) helps prevent these problems by spelling out how employees should use technology at work and what they should avoid. Here’s what to include in your policy, from personal device rules and employee monitoring to the use of artificial intelligence (AI), and how to make sure your team follows it.
An AUP is a formal workplace policy that establishes the rules and expectations for how employees and other authorized users can access and use a company’s technology, systems and information. It spells out what’s permitted, what’s prohibited and what employees are responsible for when using company resources. This can include everything from computers, mobile devices and email to cloud applications, networks and AI tools. Your policy should also make clear who must follow these rules, including contractors and temporary workers, and whether they apply to personal devices used for work.
“An AUP helps manage risk by ensuring compliance with legal and regulatory requirements, especially in industries that handle sensitive data, such as healthcare,” explained Katrina Rosseini, founder and principal of KRR Ventures Advisory. “It sets clear boundaries for acceptable use while proactively protecting against data breaches, cybersecurity threats and legal liabilities, ensuring proper technology use in the workplace.”
Beyond setting rules, an AUP helps employees understand good information security and data management practices, along with the consequences of misusing company technology.
Sam McMahon, director of IT and security at Valimail, added that an AUP is also a tool for aligning employee behavior with security, compliance and operational goals. “A strong AUP should be clear, practical and adaptable, reflecting both the technical and cultural realities of how your team operates,” McMahon said.
Keep in mind that while a written policy can help establish expectations and support enforcement, its legal effect depends on how it’s written and implemented, as well as on applicable laws.
Like your remote work policy and attendance policy, your AUP should be written clearly and in plain language. The more understandable your official policies are, the more effective they’ll be.
An acceptable use policy and an end-user license agreement (EULA) both establish rules for using technology, but they serve different purposes. An EULA is a legal agreement between a software provider and the person or organization using its software. It typically covers licensing terms, installation limits and restrictions on copying or distributing the program. An AUP, on the other hand, establishes rules for how people can use a company’s technology, networks or services.
Both can apply outside the workplace. For example, consumers may encounter EULAs when installing software, while schools, internet service providers and online platforms often use AUPs to establish rules for accessing their networks and services.
When employees use company computers, personal devices, email and online applications throughout the workday, there are plenty of opportunities for something to go wrong. Someone might download an unsafe program, share sensitive information through an unapproved app or connect to an unsecured network while working remotely. An AUP helps businesses manage these security and cyber risks by establishing clear rules for how employees should use technology. McMahon said having these guidelines in place also helps prevent confusion and misunderstandings about what’s expected of employees.
Your AUP should also explain how employees can report security concerns and what may happen if someone violates the rules. Along with employee training, access controls and incident response procedures, it can help demonstrate that your business takes information security seriously.
“Defining how employees are permitted to utilize company-owned technology … helps the IT shop better understand and predict servicing and replacement budgets,” said Evan Dornbush, founder and CEO of DesiredEffect.io and a former NSA cybersecurity expert. “It helps the security team detect abnormalities [that] could be indicative of an intruder … In some cases, it can help owners secure better insurance rates.”
Of course, having a written policy doesn’t guarantee compliance, prevent every security breach or eliminate legal liability.
A well-written AUP goes beyond establishing rules for using company technology. It can also help employees make better decisions, protect sensitive information and give your business a clearer way to address problems when they arise. Here are some of the biggest benefits:
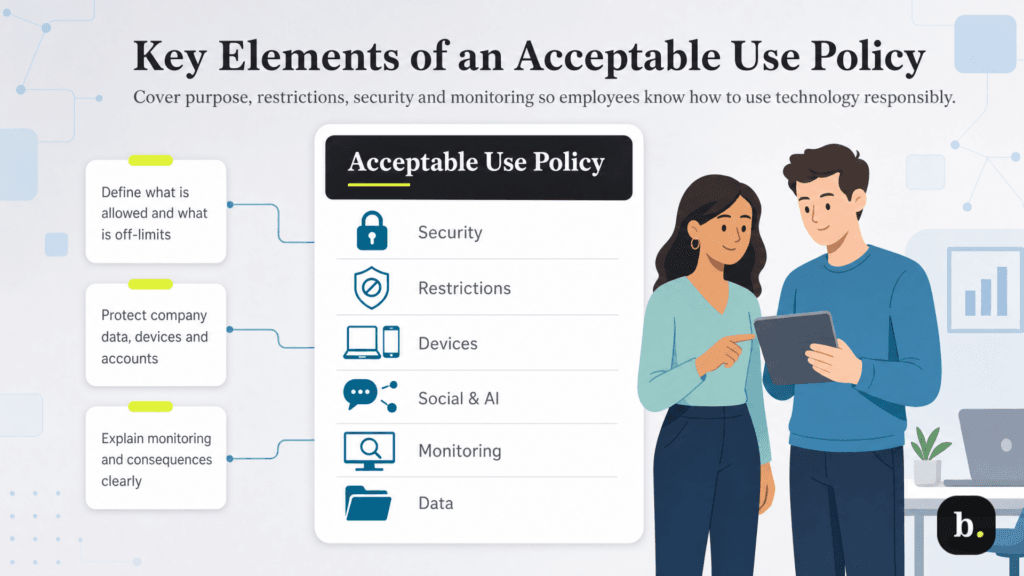
Every business has different technology needs, but there are several key elements you’ll want to address in your AUP.
Start by explaining why your business needs an acceptable use policy and what you hope to accomplish with it. For example, you might want to protect sensitive customer information, prevent unauthorized access to company systems or make sure employees understand how to use workplace technology responsibly. Giving employees some context for these rules can help them understand why they’re important rather than seeing them as just another set of restrictions.
This section should also identify who the policy applies to and which devices, networks and systems it covers, including personal devices used for work, if applicable.
Your AUP should spell out which activities are prohibited when employees use company technology, networks or systems. Be specific so there’s little room for confusion about what’s allowed. Common restrictions include:
You can also establish rules for accessing certain websites, using company email and handling other activities that may pose security risks.
Employees often need to download new programs or try different online tools to get their work done, but not everything they find is safe to use. Your AUP should establish security practices for installing software, along with rules for browser extensions, cloud services and other tools that connect to company accounts. It’s also helpful to maintain a list of approved programs so employees can easily check what’s allowed and when they need to ask permission.
Make it easy for employees to request new software or services. Before approving a tool, your IT team or designated administrator should review what information it can access, how it handles company data and who will be responsible for maintaining it. Your policy should also explain who handles software updates and make clear that employees aren’t allowed to turn off antivirus software or other required security protections.
Give employees examples of tools that require approval, such as browser extensions that can read webpage content or AI meeting assistants that record and transcribe conversations. Even free tools can gain access to sensitive company information.
Whether employees work from home, in the office or a combination of both, some may prefer to use their personal smartphones, laptops or tablets for work. If your business allows this, your AUP should explain which devices employees can use, what company information they can access and what security precautions they must take. These rules should also work alongside any separate bring-your-own-device (BYOD) or remote work policies your business has in place.
Ivan Kot, senior director of digital commerce at Itransition, emphasized the security concerns that come with allowing employees to use personal devices. “Employees often use their personal devices while accessing global and corporate networks through their private channels,” Kot said. “This raises cybersecurity risks dramatically and exposes corporate infrastructures to external intrusions. In this situation, acceptable use policies are the key documents stipulating acceptable and secure ways for employees to use corporate and personal resources for work-related purposes.”
When developing your BYOD and remote work rules, make sure you address the following:
Your AUP doesn’t have to prohibit all personal use of company-issued devices. For example, you might allow employees to use weather apps and other approved, low-risk applications while restricting apps that could compromise company security.
Your AUP should explain how employees can use social media and browse the internet during work hours. For example, you might allow occasional personal browsing while restricting activities that interfere with work or put company information at risk. Make it clear who’s authorized to post on behalf of your business and which employees need social media access as part of their jobs. You should also address inappropriate online behavior, such as harassing co-workers, impersonating the company or sharing confidential customer information without permission.
Be careful not to restrict employees’ legal rights when setting these rules. The National Labor Relations Board explains that employees may have the right to discuss pay, benefits and working conditions on social media, even if they aren’t union members. Have HR or legal counsel review your policy to make sure its restrictions don’t interfere with these protected activities.
If your business monitors employee activity, your AUP should explain what you’re tracking and why. This includes which devices and systems are monitored, what information is collected and who can access it. Employees should also know how long monitoring records are kept and whom to contact if they have questions or concerns. Be specific about the tools you use, whether that’s remote monitoring and management (RMM) software for maintaining company devices, routine security logging or more direct employee monitoring, such as website activity tracking, screenshots or keystroke logging.
Make sure your actual monitoring practices match what’s outlined in your policy. Depending on applicable laws, you may need to notify employees or obtain their consent before monitoring begins. Having employees sign an AUP doesn’t automatically give your business the right to monitor everything they do.
Employees should know what to expect if they violate your AUP. Depending on the seriousness of the violation, you might require additional training, issue a warning, restrict access to company systems or take disciplinary action, including termination. Your policy should also explain how you’ll look into possible violations and give employees a chance to tell their side of the story.
How you handle a violation should depend on what happened. For example, there’s a big difference between an employee who accidentally shares a confidential file and immediately reports it and one who knowingly steals company information. Take those differences into account when deciding what action to take, while following your company’s disciplinary procedures.
The consequences outlined in your AUP should also be reflected in your disciplinary action policy so employees know what to expect.
With employees increasingly using AI to write emails, summarize documents, analyze data and handle other everyday tasks, your AUP should set some ground rules. Employees need to know which tools they can use, what information they can share and where human oversight is necessary.
Here are some important AI issues to cover in your AUP:
McMahon emphasized the importance of setting boundaries for AI use. “Lay out rules for avoiding input of sensitive data into AI platforms, verifying AI-generated content and maintaining transparency when using AI-driven work products,” he said. “Clear guidelines ensure employees understand the risks and benefits of AI while safeguarding company information and reputation.”
Your employees handle all kinds of business information, from customer records and financial documents to employee files and internal communications. Your AUP should explain how to protect that information, where it can be stored and what employees should do if something goes wrong.
“Require encryption for sensitive data in transit and at rest to prevent unauthorized access,” Rosseini advised. “Define data retention periods and secure disposal methods for physical and digital data to protect against unauthorized access.”
To put these security measures into practice, make sure your AUP covers the following:
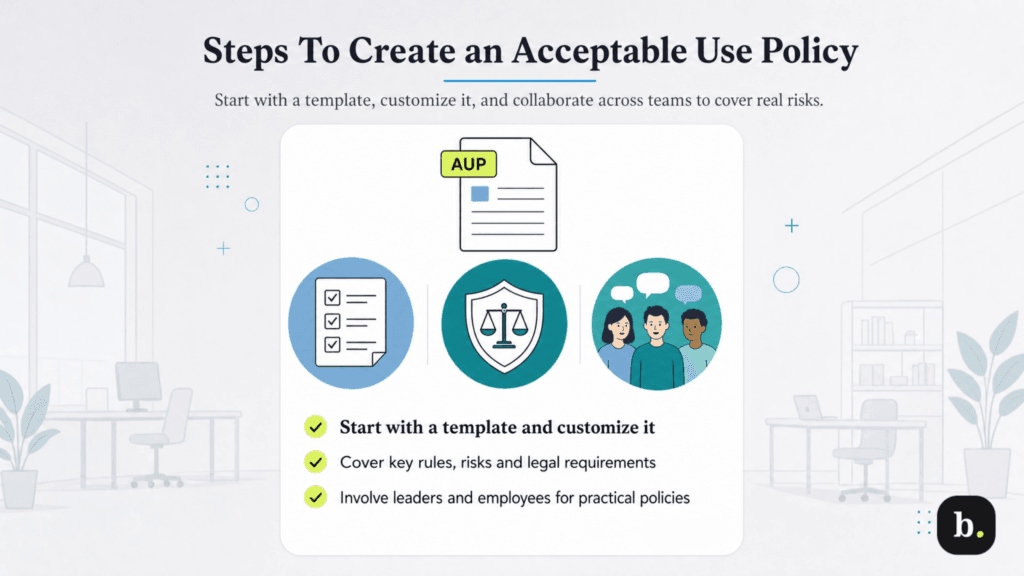
There’s no single acceptable use policy that works for every business. Your AUP should reflect the technology your employees use, the information they handle and the security risks your company faces. You’ll also want to think about how the rules will affect employees’ day-to-day work and whether they’re practical to follow.
Once you have a good idea of what your policy needs to cover, follow these steps:
Writing an acceptable use policy is only the first step. You also need to make sure employees understand the rules, know where to find them and follow them in their everyday work. Here are some ways to make your AUP more effective:
Make sure employees know where to find the latest version of your AUP. Consider keeping it in a shared employee handbook or company intranet so everyone can easily check the rules when questions come up.
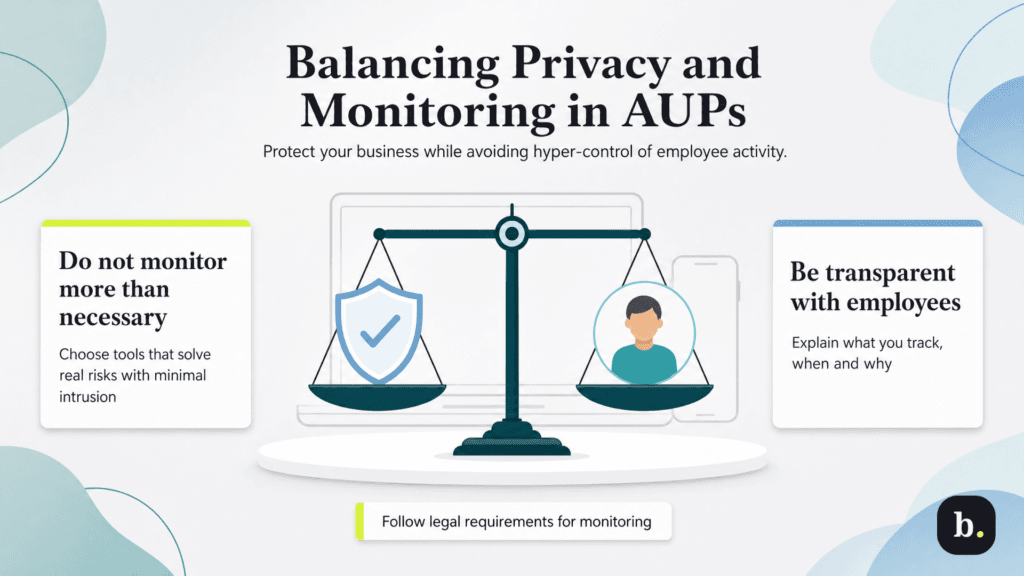
User activity monitoring software can help you enforce your AUP, but how much monitoring is too much? Employees may understandably be uncomfortable with software that tracks their every move, particularly when they’re using personal devices for work.
“Individual privacy and freedom remains one of the most disputable issues of AUP,” Kot explained. “Some companies choose to monitor their employees’ devices 24/7 without leaving a chance for private use. Others prefer to determine each and every way employees should perform their work, which deprives employees of any flexibility in their actions.”
When deciding how to monitor employees, keep these considerations in mind:
Ultimately, your goal should be to protect your business without making employees feel that every action is being scrutinized. Kot encourages business owners to “opt for a reasonable AUP while staying away from hyper-control and setting unnecessary boundaries in employees’ daily work.”
An acceptable use policy (AUP) explains how employees and other authorized users can use a company’s computers, networks, software and information. It outlines what’s allowed, what’s prohibited and what employees should do if they encounter a security problem. It should also explain any employee monitoring practices and what happens if someone violates the rules.
An AUP helps employees understand what’s expected of them when using company technology, reducing the risk of security breaches, inappropriate use and other workplace problems. It can also help businesses protect sensitive information, maintain productivity and meet applicable security requirements. While an AUP can’t prevent every problem or eliminate legal liability, it gives employees clear guidelines to follow and businesses a way to address violations.
Terms of use, sometimes called terms of service, establish the rules and conditions for using a company’s website, software or online services. An AUP focuses more specifically on what users are and aren’t allowed to do when accessing those services or other technology resources. An AUP may be included in a company’s terms of use, but businesses can also have separate AUPs that apply to employees and contractors.
Businesses enforce AUPs by training employees on the rules, having them acknowledge the policy and addressing violations when they occur. Some companies also use monitoring software and other security tools to identify potential problems, although monitoring must comply with applicable laws. Consequences can range from additional training or a warning to termination, depending on the seriousness of the violation and the circumstances involved.
Max Freedman and Jennifer Dublino contributed to this article. Source interviews were conducted for a previous version of this article.