A stolen password or convincing fake invoice can leave your business unable to serve customers, pay employees or protect sensitive information. Cybercriminals also use artificial intelligence (AI) to help carry out attacks, while businesses introduce new risks through the AI tools they adopt. We explain the cyber risks your business faces, the steps that reduce your exposure and how insurance can help with the financial consequences.
What is cyber risk?
Cyber risk is the possibility that a problem affecting your technology or data will cause financial loss, businessl disruption or other harm. It includes cyberattacks, employee mistakes and failures involving service providers. A security incident can also damage your brand’s reputation if customers lose confidence in how you protect their information.
A cyber incident can expose confidential records, interrupt operations or give criminals access to your accounts. Attackers may demand money to restore access or threaten to publish stolen data. An outage or accidental disclosure can cause harm even when no hacker is involved.
This is why you need to have the right cybersecurity. With just a computer and internet connection, anyone, anywhere, can launch a phishing attack or leverage artificial intelligence (AI) for more sophisticated crimes. “This universality makes every unsolicited email, text or social media message a potential threat,” said Dr. Arun Vishwanath, author of “The Weakest Link.”
Any business that transmits sensitive information between computers on a network connected to the internet is at risk of a cyberattack. One way to limit potential damage is to have a policy of data minimization — keeping only the data you need and allowing staff to access only the data they need to do their job. Then, if someone does hack into your network, they’ll be limited to seeing only what the user whose credentials have been compromised can see.
What are the types of cyber risks?
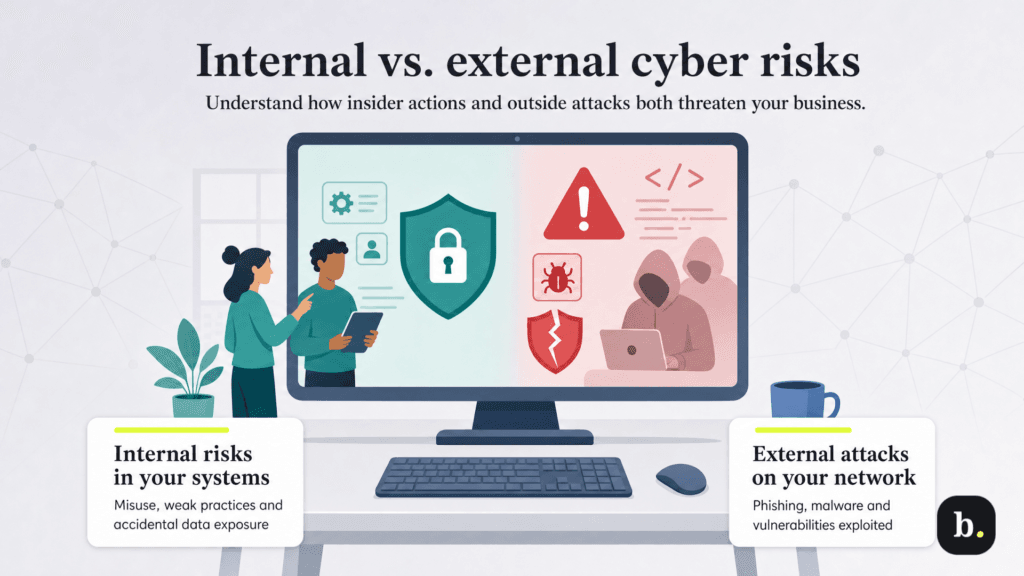
Cyber risks are not limited to external threats from bad actors. A business must also deal with internal threats that can compromise data or systems.
Internal cyber risks
Internal cyber risks can arise from deliberate misuse or everyday mistakes. Current employees, contractors and former staff members with active accounts may all have access to your IT systems and can use that access in an adversarial way. These risks could also arise as a result of a lack of awareness and poor training.
These are some common internal cyber risks to be aware of:
- Employee sabotage and theft: Employee fraud and disruption can be committed by a current or former employee who accesses your systems to obtain information to harm the company. Some information may be used to poach employees while other information could damage your business if it’s disclosed in public forums.
- Unauthorized access: Staffers could obtain access to systems they shouldn’t have access to. They may change the permissions of others or deactivate network security tools.
- Unsafe business practices: When network servers are left in unlocked rooms or users are not properly logging off devices, businesses are left vulnerable to attack.
- Accidental loss or disclosure: Team members may unwittingly disclose sensitive information. This could be by accidentally adding an unauthorized person to a confidential email chain or leaving a company laptop at a coffee shop.
- Bring your own device: Many businesses would not dream of allowing staff to bring in their own devices to connect to the company network because of the security risks involved but other organizations are OK with it. Beware, your network is doubly at risk if you allow this: First, poor security on the team member’s device might give hackers another way into your system. Second, any malware on the device may be transferred to your network. These are often referred to as “end-point attacks.
- Unapproved AI and cloud tools: Employees may upload confidential files to a personal AI account or share them through an unapproved app, exposing sensitive business information. AI assistants should only have access to information they need to perform tasks, with human approval required for sensitive actions such as sending money or modifying existing records.
Working at home can also introduce risks, according to Rob Pritchard, founder of The Cyber Security Expert. “The biggest disadvantage to working from home/remotely from this sort of risk perspective is that people can’t just turn to the person … [sitting] next to them and say, ‘Does this look suspicious to you?,’ or see that their boss is … across the office at their desk and clearly not trying to get them onto WhatsApp to buy gift vouchers for an important client.”
Conducting background checks on potential new hires can reduce your internal cyber risks.
External cyber risks
The other serious threats businesses face come from external cyberattacks, where bad actors attempt to steal data or compromise operations. If you’re subject to such an attack, it can be hard to tell exactly how your defenses have been breached. It can also take weeks or months before you realize you’ve been attacked. “External threats are probably much more significant,” Pritchard explained. “Ransomware gangs are very capable and don’t really care who they target as long as you have the means to pay.”
These are the most common external cyber risks:
- Password and session theft: Despite decades of warnings, many people, including system administrators, still use easy-to-guess passwords. Criminals can steal these credentials through phishing, information-stealing malware and breaches at other services. They may also steal session cookies or tokens that keep users signed in, allowing them to misuse an existing authenticated session.
- Phishing and impersonation: Fraudulent emails, messages and calls trick employees into sharing information, opening malicious files or granting access. A request can look as if it comes from a familiar colleague or service provider, so a recognizable name alone is not proof of identity.
- Quishing, smishing and vishing: These terms describe phishing through QR codes, text messages and voice communications. In recent years, quick response codes have been covered up with sticker replacements, which direct unwitting users to malicious sites where malware can be installed in a process known as quishing. Smishing uses short message service messages to trick individuals into revealing personal information and vishing involves voicemail phishing.
- Malware attacks: Malware is malicious software, including viruses, spyware and information stealers. It can arrive through a deceptive download, attachment, compromised website or software vulnerability. Malware is often downloaded during a “drive-by attack,” which involves the automatic download of malware to a person’s device when they visit an infected website.
- Zero-day exploits: These attacks target a software vulnerability before a patch is available, often before the vendor knows it exists. Security monitoring and limiting access can help reduce exposure while you wait for a patch or apply a vendor’s mitigation.
- Inadequate patch management: When software developers become aware of vulnerabilities, they release patches to fix them. However, your company is protected only if you download and install the patches.
- Structured Query Language (SQL) injection: Login pages, search boxes and feedback forms on websites use SQL. So do some HTTP headers and cookies. One way for cyberattackers to get into your system is to insert malicious SQL queries into a form that can later be used to manipulate or destroy a company database.
- Formjacking: These are similar to SQL injection, but instead of targeting the forms on a site, they inject malicious code on a website to capture information users enter, such as payment details at checkout.
- Traffic interception: It’s possible for cybercriminals to intercept and monitor data that’s sent over a computer network. They can capture a wide range of information, from personal details to login credentials.
- Man-in-the-middle attacks: Similar to traffic interception, this is when a hacker fools a user into logging on to their network. For example, if a member of your team is in a public area, like a coffee shop and attempts to connect to the shop’s free Wi-Fi, they may be logging on to a bogus network set up by a bad actor.
- Internet of Things attacks: Fridges, printers, security cameras and more now connect via Wi-Fi to computer networks. Often, the security on these devices is low because companies don’t see why a hacker would target them. The reason they do is because they can use them as funnels to gain access to your wider network.
- Malvertising: Criminals abuse online advertising to send users to malicious sites or deceptive downloads. An ad can lead to a fake software update or login page.
- Cross-site scripting: These attacks take advantage of vulnerabilities in web apps to run malicious scripts in users’ browsers. For example, if you allow customers to talk to each other via an online forum, a hacker might insert bad code into a forum post that then triggers an action in the browser of another customer using the forum. They can hijack user accounts with this approach, including users with admin privileges.
- Watering-hole attacks: This is when attackers go after commonly used resources shared by specific groups of users. For instance, many people in your company may log in to a social media network like LinkedIn or a vendor portal. Cyberattackers can insert malicious scripts into these sites, infecting your users’ computers when they next visit them.
- Distributed denial-of-service (DDoS) attacks: Attackers overwhelm a website or service with traffic or requests so legitimate users cannot access it. These attacks often use networks of compromised devices.
- Cryptojacking: Criminals use your devices or cloud resources to mine cryptocurrency without permission. This can slow systems and generate unexpected computing or electricity costs.
- Ransomware and data extortion: Ransomware can encrypt files or disrupt systems, while attackers may also steal data and threaten to release it. Cyberextortion can occur without encryption. Paying does not guarantee recovery or deletion of stolen data, and the FBI discourages ransom payments.
- Trojans: A Trojan disguises malicious software as a legitimate program or download. Once installed, it may steal information, create remote access or install additional malware.
- Supply-chain and third-party attacks: Criminals can impact a business through compromised software, service providers or connected accounts. For example, companies sometimes require clients to place orders with them or send invoices for work done via a custom app that’s updated regularly. In a supply-chain attack, hackers target this type of program so hundreds or thousands of businesses and clients may end up downloading the infected app when a new update is rolled out.
- Prompt injection: Malicious instructions hidden in a document, webpage or message can manipulate an AI assistant that processes that content. An assistant connected to business systems could then disclose information or attempt an unauthorized action. This risk makes restricted permissions and approval steps particularly important.
The 2026 Verizon Data Breach Investigations Report found that vulnerability exploitation accounted for 31 percent of breaches in its reporting dataset. Ransomware appeared in 48 percent, and third parties were involved in 48 percent.
Conducting a cyber risk assessment and consulting an IT professional can help you understand your business’s vulnerability to a cyberattack.
What is the financial impact of cyber risks?
The potential financial impacts of cyber risks on a company are huge. Even a minor attack can force a business to pay for lost or stolen data records. IBM’s 2026 Cost of a Data Breach Report puts the global average breach cost at $4.99 million, up 12 percent from the previous year.
“A cyberattack can drive a small business into bankruptcy or total failure,” said cybersecurity, privacy and AI expert Joseph Steinberg. “Unfortunately, such a claim is not theory – we have seen it happen many times. A cyberattack can easily destroy confidence in a small business, causing it to lose customers, while simultaneously inflicting a severe enough cash flow problem as to render the business unable to meet payroll obligations.”
Even if the financial consequences are not as high for a small business, smaller companies still need to brace themselves for lost revenue due to a compromised operating system being shut down for days or weeks. Plus, even after a business restores all systems, consumers may be wary of working with a company that recently experienced a data breach or cyberattack, afraid that their personally identifiable information is not safe. That, too, will impact your bottom line.
Costs may include incident investigation, system restoration, lost sales, legal advice, required notifications and support for impacted customers. Payment fraud can also cause a direct cash loss. Estimate how long your business could operate without email, payment processing or its main software, then use that estimate to prioritize recovery spending.
How can companies reduce their cyber risks?
Creating a cybersecurity plan gives your team a practical way to reduce risk and prepare for incidents. While you can’t prevent every cybercrime, you can do a lot to ensure your business is not harmed. Here are 13 ways to reduce your company’s cyber risk:
- Update your computer systems, browsers, apps and other programs regularly: When you don’t update, gaps begin to form that allow things like malware to infiltrate your system. Make sure your antivirus security is up to date and regularly update your operating system to prevent these gaps from forming.
- Replace software and equipment that’s no longer being updated: If something you’re using is no longer being updated, talk to your team about switching to a new product. Track end-of-support dates and plan replacements before security updates stop. Include routers, firewalls and connected devices, not just desktop software.
- Control outgoing data and app connections: Use approved sharing tools and review public links, third-party integrations and AI access. Set rules for what employees may upload or send outside the business, and remove connections you no longer need. [Read related: how to protect sensitive information]
- Train your employees: Make sure your employees understand what cybersecurity risks exist and how to be on the lookout for them. This is especially true for things like phishing schemes that may be received by gullible workers who haven’t been trained not to click on suspicious links.
- Develop strong passwords and use a business password manager: Create complex passwords that cannot be guessed. Make sure your system administrator’s password is different from the server’s password. You don’t want to make it easier for hackers to gain access to the entire server. You may also want to consider using a reputable app to manage users’ passwords across the business.
- Encrypt sensitive information: When sending or storing data, encrypt it. This means data isn’t saved in a normal text format, making it harder to be misused. As more companies use off-site servers, cloud encryption is particularly important, as the transmission of data between your network and your cloud provider is another potential attack vector.
- Limit login attempts: Hackers will use bots to work on cracking passwords indefinitely. You can stop them by limiting the number of login attempts allowed to access your data or server systems.
- Require multifactor authentication: This is similar to the technology where banks and credit card companies text you a four- or six-digit code to verify your identity when you make a purchase online. You can set up your computer system so that whenever a colleague logs in, they have to provide an additional form of verification, such as a unique numerical code.
- Implement a kill switch: A kill switch allows an IT professional to shut down all access to servers or pull websites offline when a threat is detected. This gives you time to address the threat before it can do any damage.
- Reduce payment data exposure: Don’t risk a hacker collecting your customers’ credit card data. Never store this sensitive information in any database you maintain and enact strict policies so your employees never do it either. Use a payment provider’s hosted checkout or tokenization where practical instead of retaining card numbers yourself.
- Back up your data regularly: Take the time to conduct regular data backups. This will make restoration much easier if you do fall victim to a cyberattack.
- Maintain an inventory and enforce access limits: Regardless of whether you allow staff to use their own devices, consider setting up a register of permitted devices. This means no unauthorized (unregistered) device can log in to your network. You’ll also be able to use the registry to quickly restrict access so former employees and contractors can no longer gain entry.
- Set up a separate public network: Particularly in the leisure and hospitality sectors, customers today expect you to provide free Wi-Fi access. Offering it can give you a competitive advantage, but you should provide it over a separate network that doesn’t use the business Wi-Fi your team uses to manage sensitive data. [Find out how to set up business Wi-Fi.]
Small and medium-sized businesses’ budgets for cybersecurity vary in complexity and cost depending on the types of risks individual companies face. If you don’t have an IT department or are not confident with IT as an owner, you should call in a cybersecurity expert to advise you on creating a cybersecurity plan, setting an appropriate budget and rolling out protections.
What should you do if your business suffers a cyberattack?
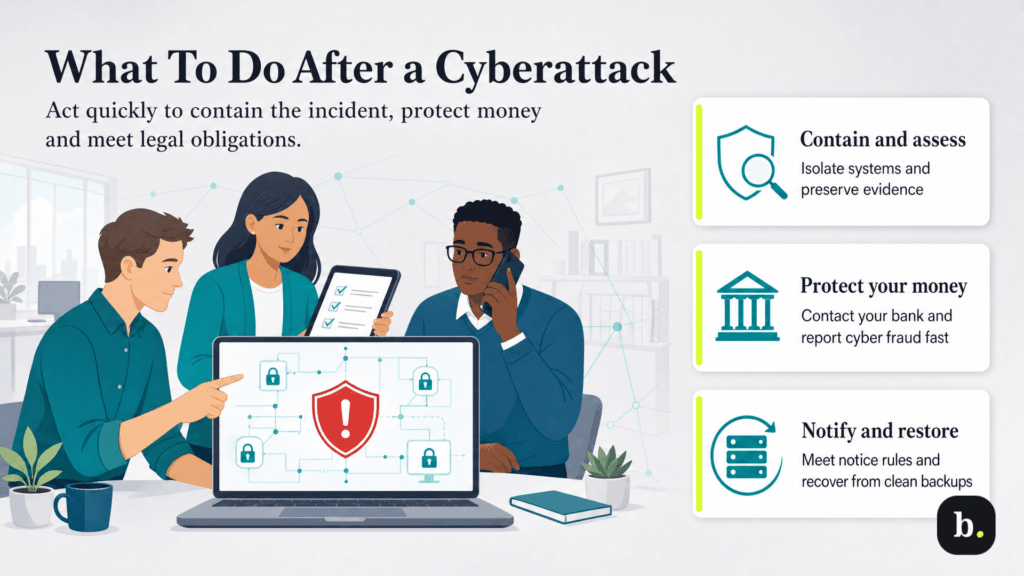
Activate your response plan as soon as you suspect an incident. Notify your IT or security provider and your insurer’s breach hotline, if you have one. Use a separate, trusted communication channel if your email or collaboration tools may be compromised.
- Contain the problem and preserve evidence. Have your response team isolate affected devices and accounts. Avoid wiping or reinstalling systems before investigators preserve relevant evidence. The FTC’s breach response guide recommends taking affected equipment offline while preserving it for forensic investigation.
- Contact your bank immediately if money was sent. Request a recall or other available intervention and report the fraud to the FBI’s Internet Crime Complaint Center. Prompt action matters, although recovery is not guaranteed.
- Determine what was affected and who must be notified. Work with qualified legal counsel and incident responders to identify the systems, data and people involved. Track legal deadlines and contractual notice requirements, including obligations to customers and business partners.
- Restore safely and address the entry point. Recover from verified backups after containing the incident and correcting the cause. Review compromised accounts, sessions and app permissions before reconnecting systems. Document what happened and update your response plan.
How can cyber liability insurance help?
Cyber liability insurance can help pay for specified losses and response expenses. First-party coverage addresses your business’s own losses, while third-party coverage addresses certain claims brought against it. Depending on the cyber insurance policy, covered costs may include:
- Lost income and extra expenses from a covered business interruption
- Ransom demands
- Attack investigations and data or system restoration.
- Crisis communications and public relations support
- Regulatory fines or penalties
- Customer notification costs (which can range from 50 cents to $5 per person) and related support services
- Customer credit monitoring or identity protection services
- Legal defense, judgments or settlements for covered claims
On top of paying for losses and damages, many insurers will help businesses remediate their losses as quickly as possible. This means they use their internal teams to help halt the progress of viruses and malware, with the goal of minimizing the ultimate costs to both your business and them.
Cyber insurance applications may ask about multifactor authentication, backups, access controls and patching. Make sure your answers accurately describe the safeguards you have in place, and review them when you renew.
Can you be penalized for cyberattacks?
A cyberattack does not automatically mean your business broke the law. Legal exposure depends on the rules that apply to your business, the security measures you maintained, how information was handled and your response. An investigation may examine whether you met duties to protect information or notify affected parties.
The Federal Trade Commission (FTC) advises businesses to keep only the personal information they need, protect it and dispose of it securely. State privacy and breach notification laws may also apply, along with sector-specific federal requirements. Work with counsel to identify your obligations before an incident occurs.
Potential consequences can include regulatory enforcement, civil penalties, lawsuits and contractual claims. Criminal liability involves separate statutory requirements; being the victim of an attack does not automatically expose an owner to jail time. There is no single fine schedule or notification deadline that applies to every business and every breach.
Here are some of the penalties your business could face:
- Fair and Accurate Credit Transaction Act fines can range from $100 to $1,000 per consumer for willful non-compliance.
- The FTC penalties can exceed $50,000 per day.
- Health Insurance Portability and Accountability Act penalties for criminal wrongful disclosures are up to $50,000 plus one year in prison for basic violations.
- Individual states all have their own data breach laws, with Florida charging up to $500,000 for businesses not meeting notification requirements and Michigan capping multiple violation penalties at $750,000.
Most small companies can’t afford these types of fines, nor can they afford to lose an estimated 20 to 30 percent of their customer base from the fallout of a data breach. Keeping consumer data private and having insurance to help protect against financial losses are critical in the digital age.
Who commits cybercrimes?
Cybercriminals come from various backgrounds. Some cybercrimes are committed by former employees looking to get revenge on a business that fired them. You can prevent this type of crime by revoking system access as soon as an employee is terminated.
Sometimes, attacks come from industry rivals trying to steal your commercial secrets or find information to portray your business in a negative light. There are also activist organizations that believe they are helping society by hacking and harming certain companies.
Some security risks simply arise from careless mistakes made by employees, especially those who work for businesses that haven’t implemented the right security policies and training. Still, the majority of cybercrimes are committed by those who intend to profit from hacking by selling data on the dark web, demanding a large ransom or funneling credit card transactions to a third-party account they control.
Neil Cumins and Kimberlee Leonard contributed to the reporting and writing in this article. Source interviews were conducted for a previous version of this article.